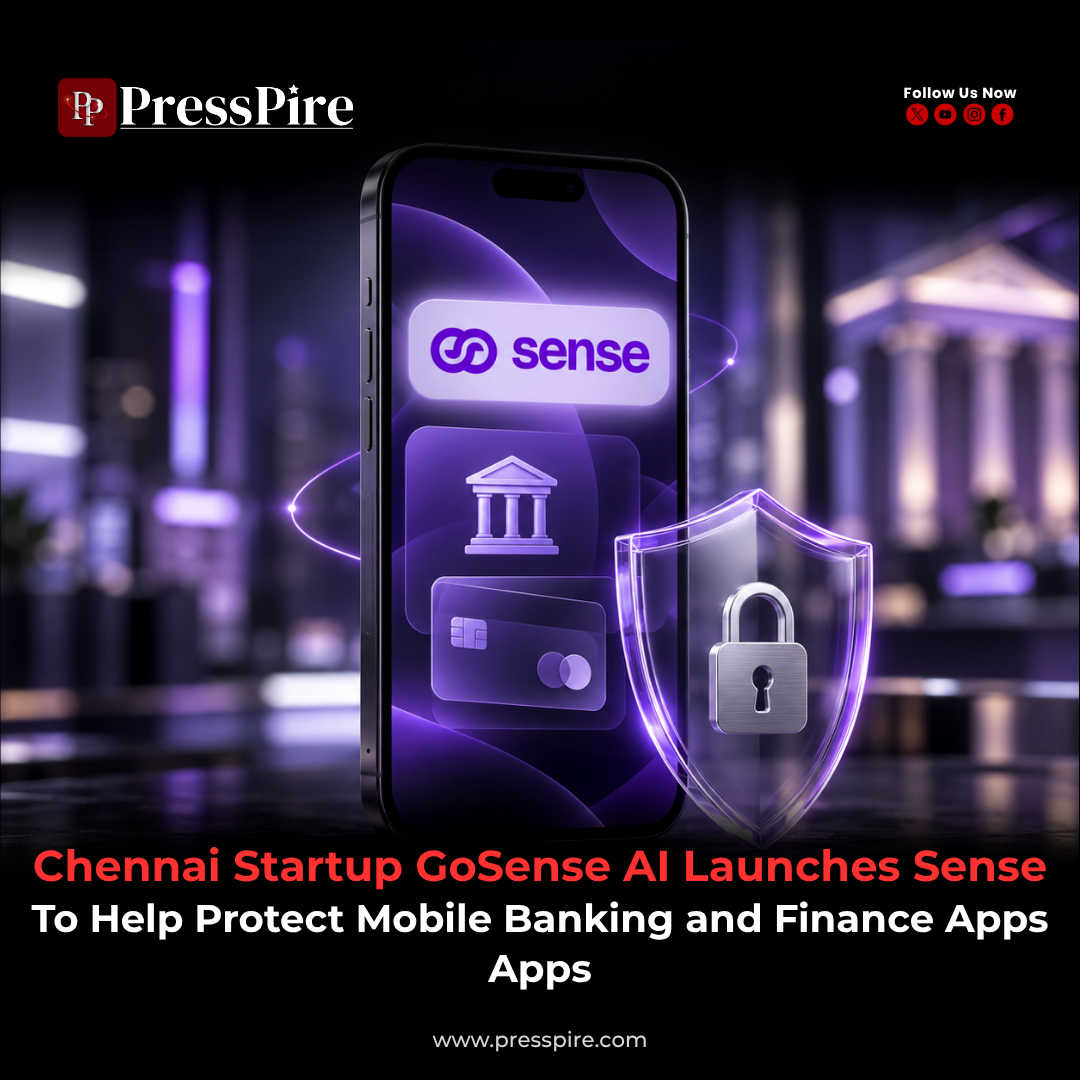
Chennai Startup GoSense AI Launches Sense to Help Protect Mobile Banking and Finance Apps
The startup is bringing device security into focus with a consumer app, alongside tools that help banks and fintechs identify suspicious activity inside their applications.
GoSense AI, a Chennai-based cybersecurity startup, has introduced Sense, a personal digital security app designed to flag suspicious activity on smartphones and add protection for the financial applications people use every day.
The company says the consumer app was launched at Global Fintech Fest 2026. Its introduction comes alongside GoSense AI’s broader work on security software for banks, fintech companies and digital payment providers.
The focus is on a practical problem: a financial transaction can begin on a phone whose applications, permissions or operating environment have been manipulated. GoSense AI aims to help identify those risks while a device or application is in use.
What GoSense AI Says Sense Can Do
Co-founder Noel Rajakumar describes Sense as an app that monitors a device in the background and flags suspicious activity, with a particular focus on the financial apps installed on it.
The intended benefit is earlier visibility into potential problems. A person using mobile banking or payment services may not otherwise recognise changes that could affect the security of their phone.
The consumer app sits alongside the company’s institutional security platform. Financial institutions can integrate that platform into their own applications and use its signals to inform security decisions.
These offerings have different roles: the consumer app provides personal device monitoring, while the institutional tools support security controls within participating banks’ and fintechs’ systems.
The Founders Behind the Chennai Startup
GoSense AI was co-founded by Muthukumar D, its chief executive officer, and Noel Rajakumar, its chief operating officer.
In statements accompanying the company’s platform announcement, the founders emphasised the need to understand activity across applications, devices and transactions as it happens.
Their argument is that financial security increasingly depends on what is happening on the customer’s phone during a session. Identifying signs of manipulation at that point could give an institution an opportunity to intervene before a suspicious payment is completed.
How Runtime Application Protection Works
A central part of GoSense AI’s institutional offering is Runtime Application Self-Protection, commonly called RASP.
“Runtime” means the period when an application is actually operating. This approach adds checks inside a running app to look for changes or activity that could undermine its security.
According to the company’s product documentation, its checks cover application integrity, the device environment and attempts to interfere with an app’s execution.
| Risk area | What the protection is intended to identify |
|---|---|
| App tampering | Changes to an application’s code, package or integrity |
| Rooted or jailbroken devices | Altered device environments that can weaken normal security boundaries |
| Emulators and cloned apps | Simulated devices or copied app environments requiring closer assessment |
| Debugging and code injection | Attempts to inspect or modify an application while it runs |
| Malicious overlays and accessibility abuse | Misuse of screen layers or device permissions to interfere with a user’s actions |
These capabilities belong to the company’s application protection offering. Their effectiveness in a particular banking app depends on implementation, configuration and testing.
Combining Device and Session Signals
GoSense AI’s platform also brings together information about devices, sessions and user behaviour to assess risk.
Its website describes signals such as a change of device, suspicious session activity and unusual changes involving payment beneficiaries. The purpose is to give financial institutions more context when deciding whether an action needs further checks.
A new device can be a routine event. Its significance may change when it appears alongside other unusual activity. This is the practical value of evaluating several signals together.
The company says institutions can configure responses such as monitoring, warnings or blocking. Its account protection tools also describe additional verification or holds on sensitive actions.
The response therefore depends on the financial institution’s policies and the way the technology is integrated.
Applications Across Banking, Payments and Digital Finance
The company is targeting a broad range of financial services, including mobile banking, UPI and payment applications, lending, wallets, cards, insurance and wealth platforms.
Its wider product portfolio includes code obfuscation, app authentication, mobile verification, bot detection and account takeover protection.
Code obfuscation makes software harder to understand through reverse engineering. App authentication helps establish whether a request is coming from a genuine application. Other tools address automated activity and suspicious account access.
Together, these functions illustrate the company’s broader business proposition: providing several security controls that financial services teams can use across their digital products.
Why the Launch Matters for Fintech Companies
For banks and fintechs, security decisions also affect the customer experience.
A system that misses malicious activity can expose users to harm. A system that repeatedly blocks legitimate activity can make everyday banking difficult and increase support demands.
OWASP, the organisation behind widely used application security guidance, treats runtime protection and anti-tampering measures as additional layers of defence. Its guidance also recognises that some device checks can produce false positives and exclude legitimate users.
For potential buyers, this makes testing across supported devices and normal customer journeys a practical priority. Detection quality, performance and clear handling of alerts will matter alongside the breadth of the advertised feature list.
Availability and the Next Stage
In his public launch post, Rajakumar said the consumer app’s download link would be shared separately. That post did not set out pricing or a complete list of supported consumer devices.
The launch coverage reviewed also did not provide independently validated figures showing reductions in fraud losses.
GoSense AI’s next challenge is to demonstrate how its consumer app and institutional tools perform in everyday use. For consumers, that means useful and understandable risk alerts. For financial institutions, it means dependable integration and security decisions that protect customers while allowing legitimate activity to proceed.
For more insights navigate: PressPire | Stories That Shape the Future
Read previous article here : ericsson-made-in-india-antennas-exports/
Follow PressPire on Facebook | Instagram | LinkedIn | YouTube
PressPire | Stories That Shape the Future