CERT-In Warns Apple Users of Security Flaw Exploited in Targeted Attacks
Technology | Cybersecurity | 4 October 2026
India’s cybersecurity agency has issued a high-severity warning about an Apple software vulnerability. Security fixes are available for affected iPhone, iPad and Mac software.
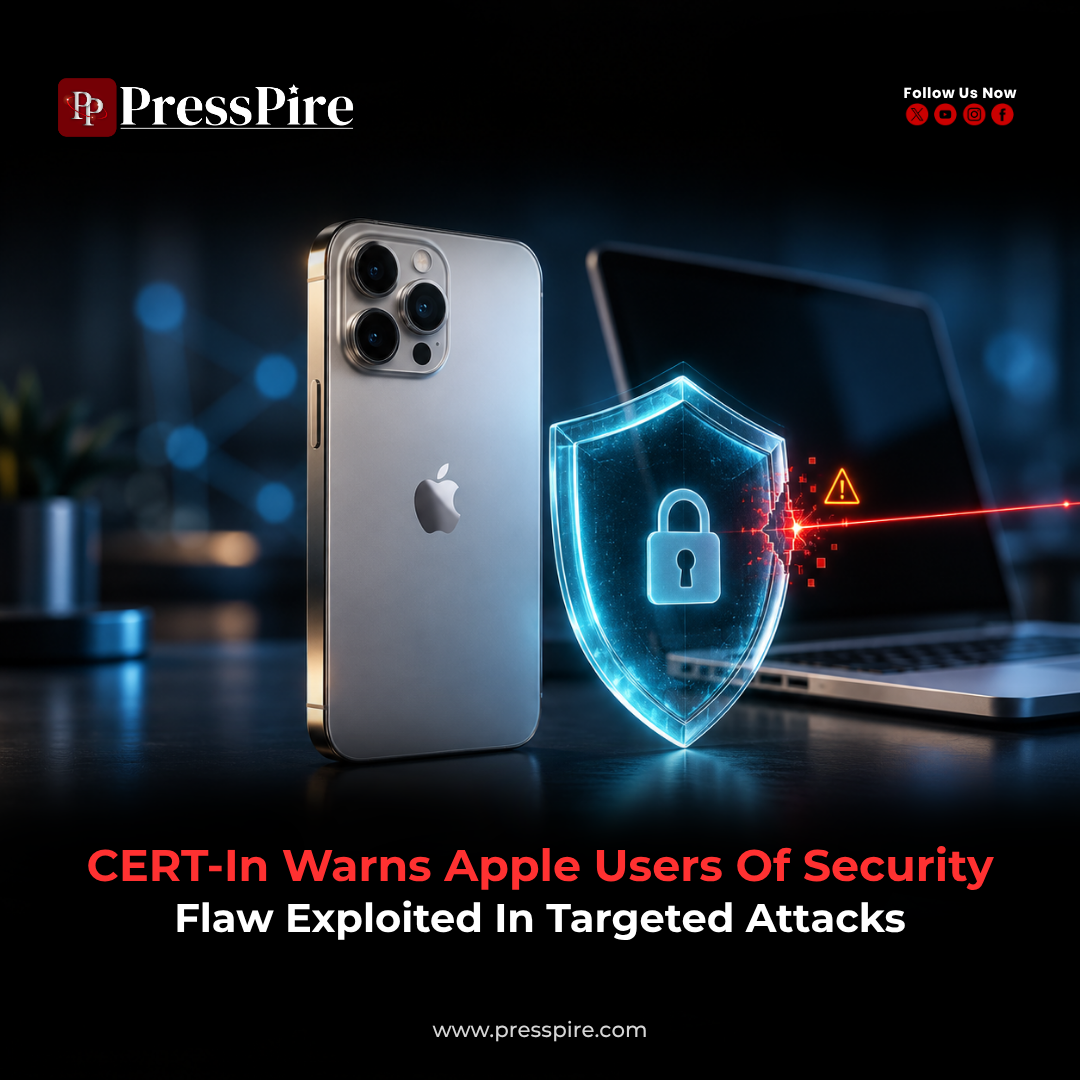
The Indian Computer Emergency Response Team, or CERT-In, has warned Apple users about a security flaw that could allow an attacker to run malicious code on affected devices. Its advisory, CIVN-2026-0485, was issued on 1 October 2026 and rates the vulnerability as High severity.
Tracked as CVE-2026-86950, the flaw affects certain versions of iOS, iPadOS and macOS. CERT-In says it is being exploited in sophisticated attacks against selected individuals and urges users to install the appropriate security updates immediately.
What is the Apple security flaw?
Apple identifies the vulnerability in CoreGraphics, a software framework used for graphics processing. The company describes it as an out-of-bounds write issue and says processing a specially crafted malicious file could lead to arbitrary code execution.
In practical terms, a successful exploit could cause the device to run instructions chosen by an attacker. Apple says it corrected the problem by improving bounds checking and credits Meta Product Security in its security notice.
CoreGraphics supports functions such as drawing, image handling and PDF processing. That explains why a graphics framework can be relevant to device security when users are working with everyday content. However, the framework’s capabilities do not establish which particular file format was used in the reported attacks.
What is known about the targeted attacks?
Apple’s wording is cautious: it says it is aware of a report that the issue may have been used in an exceptionally sophisticated attack against specific people running iOS versions earlier than iOS 27.
This distinction matters. The security notices cover iPhone, iPad and Mac software, but Apple’s published exploitation statement specifically refers to older iOS versions. It does not establish that the reported attacks also compromised Macs or every affected product.
The cited notices do not identify the victims, attackers or number of compromised devices. They also do not establish a widespread campaign against the general public.
Which software versions are affected?
CERT-In lists the following affected software. Apple’s corresponding security notices identify the releases containing the fix.
| Software | Versions listed as affected | Fixed release referenced |
|---|---|---|
| iOS | Earlier than 26.7.1 | iOS 26.7.1 |
| iPadOS | Earlier than 26.7.1 | iPadOS 26.7.1 |
| macOS Sequoia | Earlier than 15.8.1 | macOS Sequoia 15.8.1 |
| macOS Tahoe | Earlier than 26.7.1 | macOS Tahoe 26.7.1 |
These details appear in CERT-In’s advisory and Apple’s security notices.
Apple released these fixes on 28 September 2026, three days before CERT-In issued its warning. The version numbers identify patched releases within those software branches. Users should install the latest compatible update offered for their device; Apple’s release list also includes newer operating-system versions.
How to update an iPhone or iPad
Users can check their installed software version and available updates through the device’s settings:
- Back up the device using iCloud or a computer.
- Connect it to Wi-Fi and a power source.
- Open Settings → General → Software Update.
- Download and install the available compatible update, following the onscreen instructions.
Apple also provides automatic-update settings on this screen. Enabling automatic installation can help prevent future security fixes from being missed. For an urgent update, check that installation has completed. If an update does not appear, Apple provides instructions for updating through a computer.
How to update a Mac
Mac users should back up their computer, then open Apple menu → System Settings → General → Software Update. Install the compatible update offered and allow the process, including any restart, to finish.
Apple says Software Update displays releases compatible with the particular Mac model. This makes the update screen the appropriate starting point when choosing between a security update for an existing macOS branch and an available operating-system upgrade.
What should workplaces do?
For organisations using Apple devices, the practical priority is to check installed operating-system versions and confirm that applicable updates have completed.
A recommended response is to identify affected devices, coordinate installation with users and record any devices that cannot receive an appropriate update for further review. This is an operational recommendation based on the advisory’s affected-version list. The warning does not, by itself, show that a particular employee or organisation has been attacked.
Additional protection for people at heightened risk
Apple offers Lockdown Mode for the small number of people who may face unusually sophisticated, personally targeted cyberattacks. It restricts certain attachments, web technologies and other features to reduce potential avenues of attack.
Because these restrictions change how the device works, users should review Apple’s guidance before enabling it. Apple recommends updating devices to the latest software to obtain the complete available protections. The cited vulnerability notices do not claim that Lockdown Mode alone blocks this specific flaw.
Anyone receiving an Apple threat notification should take it seriously and seek expert assistance. Apple says users can verify a notification by signing in directly at account.apple.com and checking for the alert. Genuine threat notifications do not request passwords or verification codes, or instruct recipients to install apps or open files.
For more insights navigate: PressPire | Stories That Shape the Future
Read previous article here: cipla-pune-warehouse-licence-cancelled-fda/
Follow PressPire on Facebook | Instagram | LinkedIn | YouTube
PressPire | Stories That Shape the Future